apt verified the package, then a retry let somebody swap it for another
2026-11-05Security
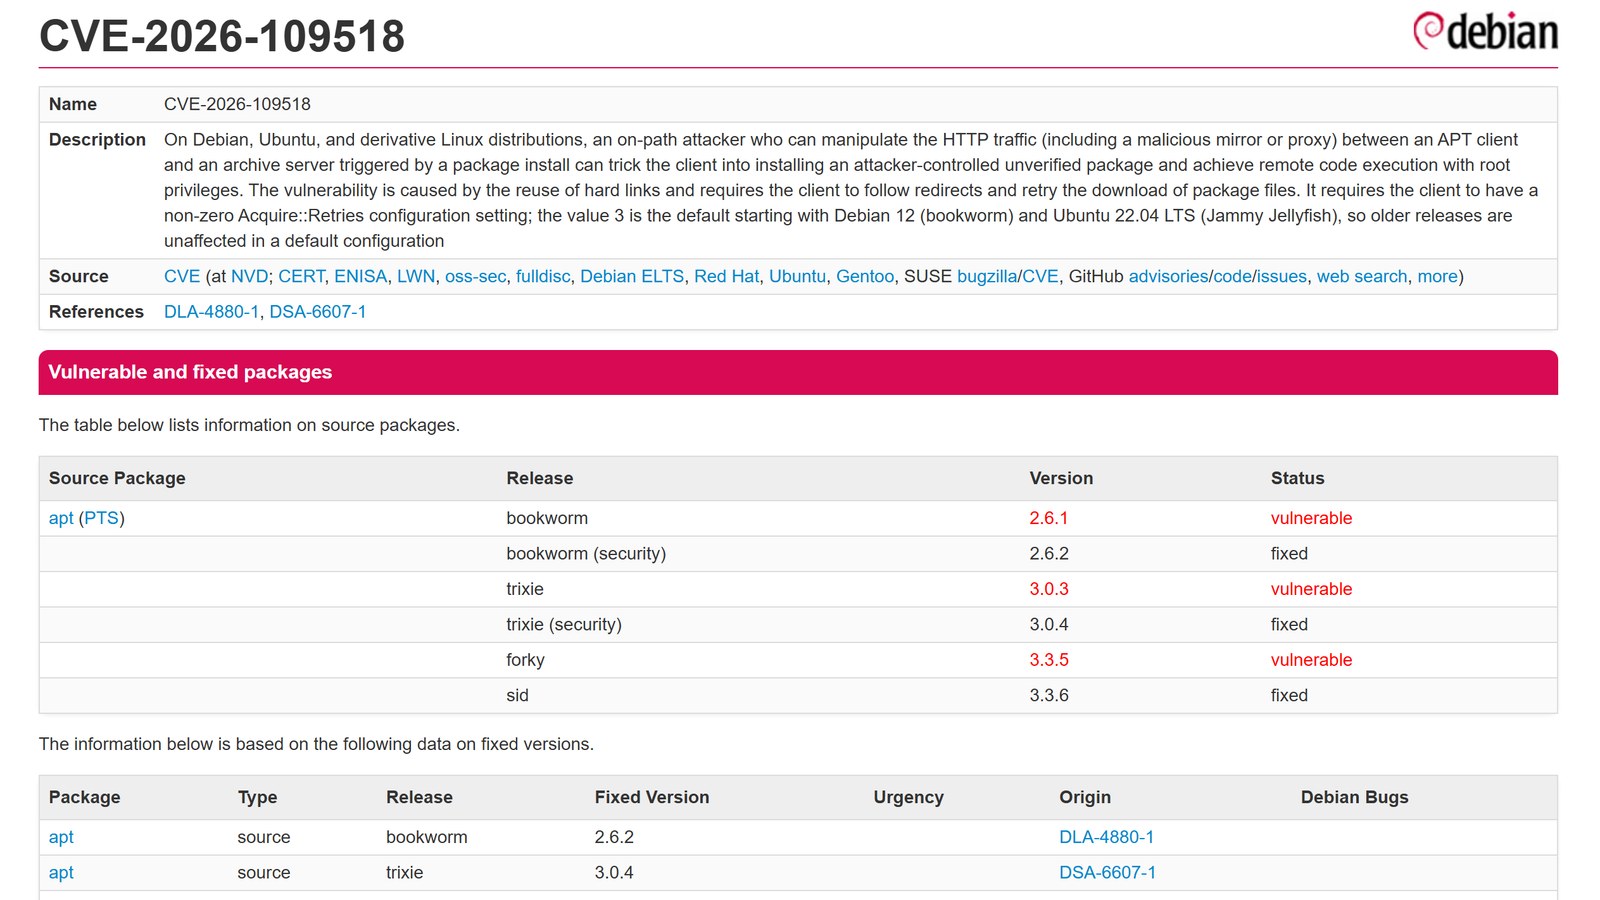
CVE-2026-109518 gives an on-path attacker root on Debian and Ubuntu machines. It needs a retry setting that has been the default since Debian 12, which means the older releases are the safe ones.