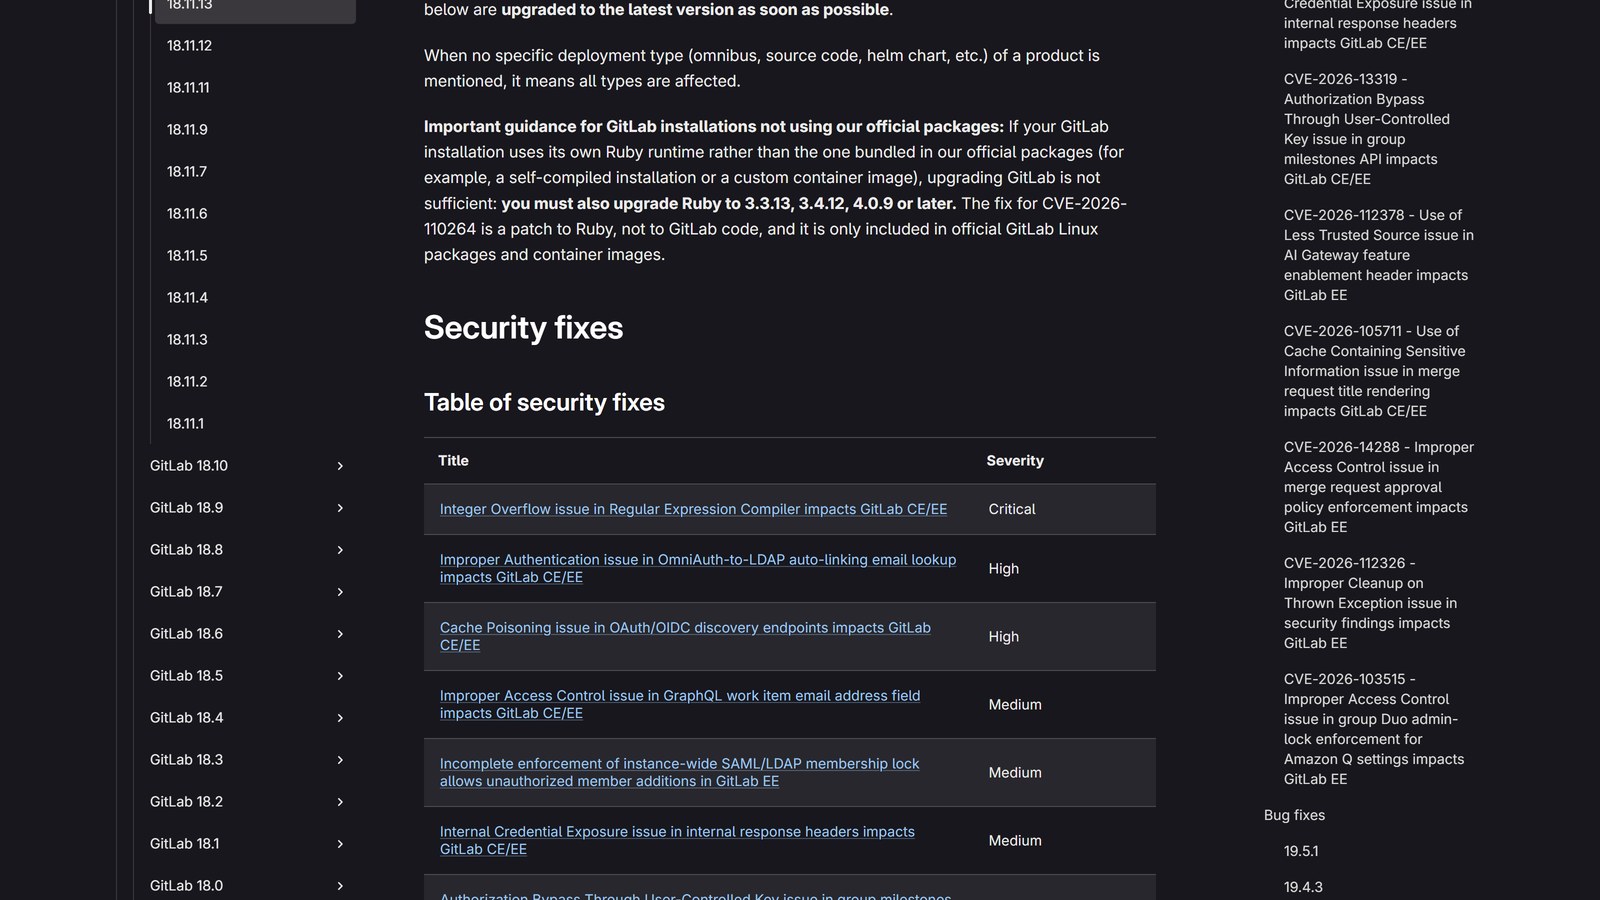
GitLab's fix for a 10.0 is a patch to Ruby, not to GitLab
2026-11-07Security
The coverage said 1,000 GitLab servers were exposed. Shadowserver's same post counted 11,300 exposed to a different bug, a CVSS 10.0 in Ruby's regex engine, and the release everyone rushed to under the CISA deadline does not contain its fix.