Skip to content
tag — patch-management

grep -rl "patch-management" ./articles

#patch-management

17 articles

CISA's three-day patch deadline did not exist before this year

2026-11-09Security

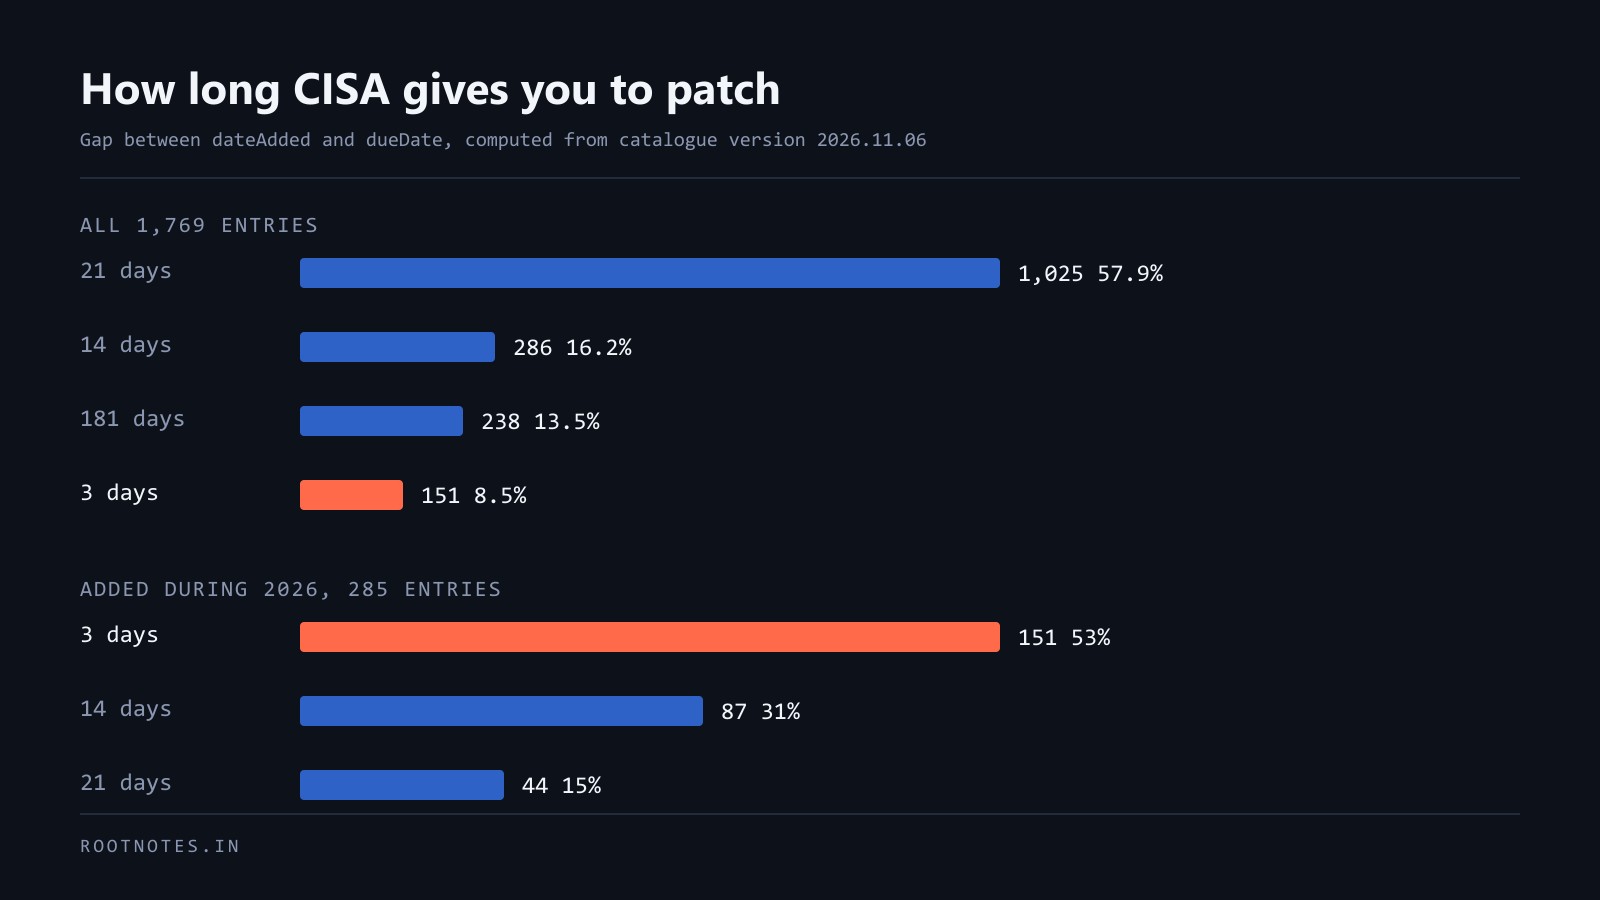
We counted the gap between the date added and the deadline for all 1,769 entries in the exploited vulnerabilities catalogue. Twenty-one days is the historic norm. Every three-day deadline ever issued was issued in 2026, and they are now the majority.

The catalogue told agencies to patch the wrong Zyxel flaw

2026-11-09Security

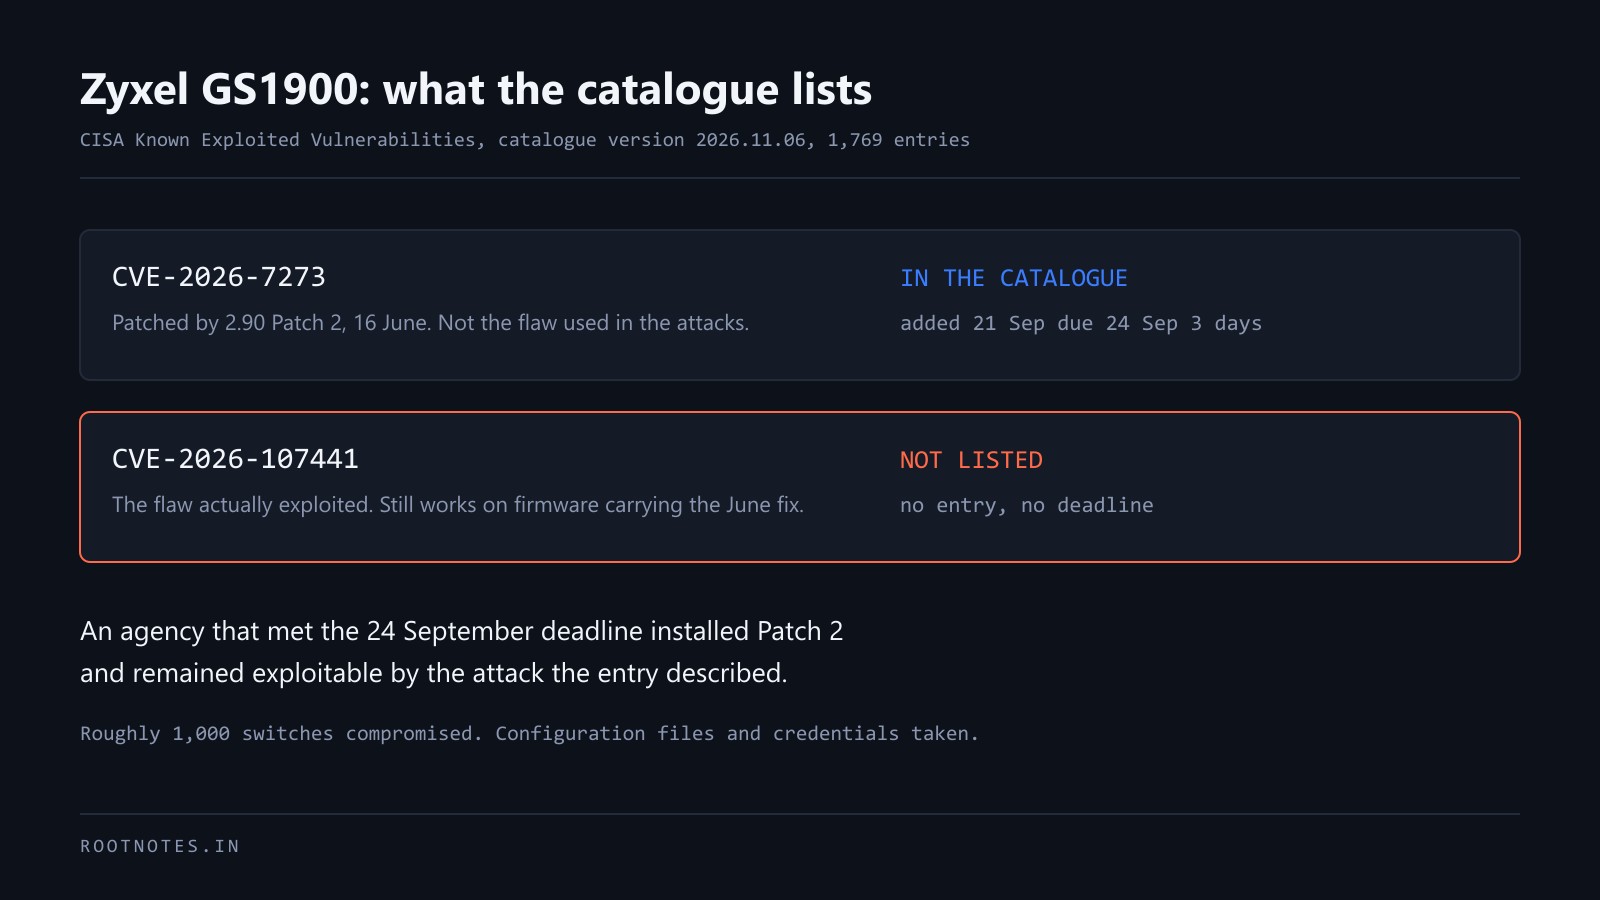
Attacks on about 1,000 Zyxel switches were blamed on a flaw patched in June. Binarly found the exploit uses a different one that still works on patched firmware. The wrong CVE is in the federal catalogue and the right one is not.

GitLab's fix for a 10.0 is a patch to Ruby, not to GitLab

2026-11-07Security

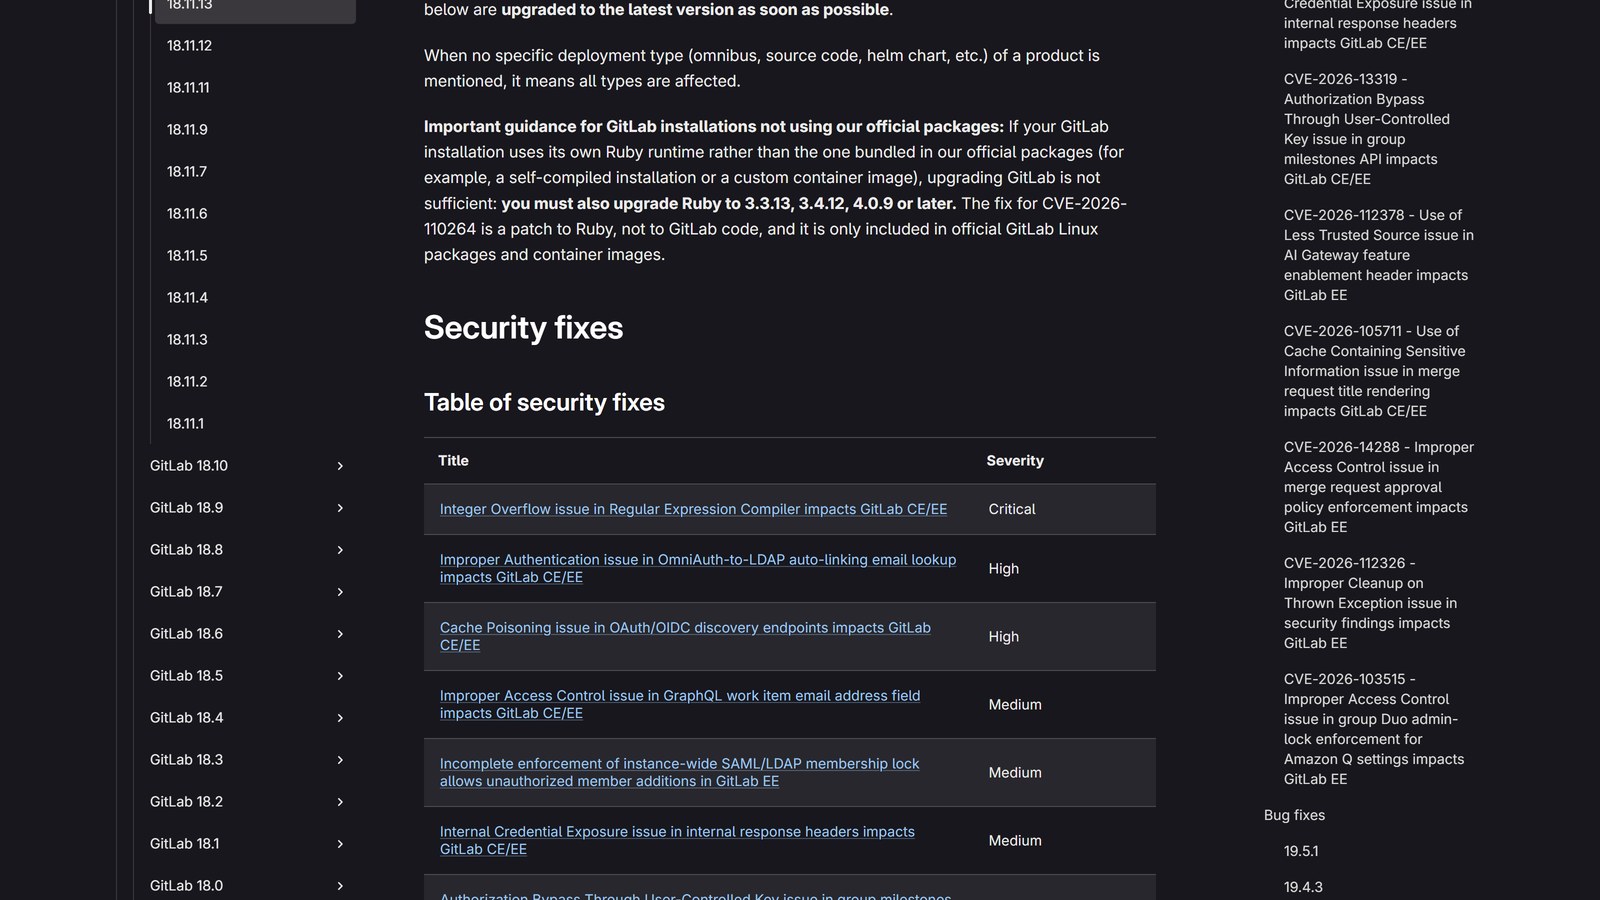
The coverage said 1,000 GitLab servers were exposed. Shadowserver's same post counted 11,300 exposed to a different bug, a CVSS 10.0 in Ruby's regex engine, and the release everyone rushed to under the CISA deadline does not contain its fix.

The NetScaler appliances restarting after the patch were not a patch bug — they were a third zero-day, and the sixth crash is the trigger

2026-10-06Security

On 3 October we wrote that Citrix customers were watching their gateways reboot after installing the emergency build, with no CVE and no root cause published. Citrix disclosed it on the 4th: CVE-2026-88779, a memory overflow reached through SAML, exploited in targeted attacks. Each attempt crashes the authentication service, and the sixth restarts the appliance.

The NetScaler build that stopped the exploitation is restarting the gateway, and the bulletin that told you to install it says nothing about it

2026-10-03Security

Citrix shipped 14.1-73.37 for two actively exploited 9.5s. Customers who installed it are reporting repeated appliance reboots, traced to crafted SAML traffic crashing the authentication service until the watchdog restarts the box. Citrix says it is tracking a newly seen SAML issue. Bulletin CTX697096, last updated 27 September, still does not mention it.

Microsoft's own figures put weaponisation under a day and remediation at up to sixty, and the most-detected flaw is from 2020

2026-10-03Security

The 2026 Digital Defense Report, covering July 2025 to June 2026, says attackers are collecting the benefits of AI first. Underneath that headline are three numbers that do not need AI to explain them: nearly 40,000 CVEs in six months, a weaponisation median well below 24 hours against 30 to 60 days to remediate, and a 2020 vulnerability still responsible for most detections among the top five.