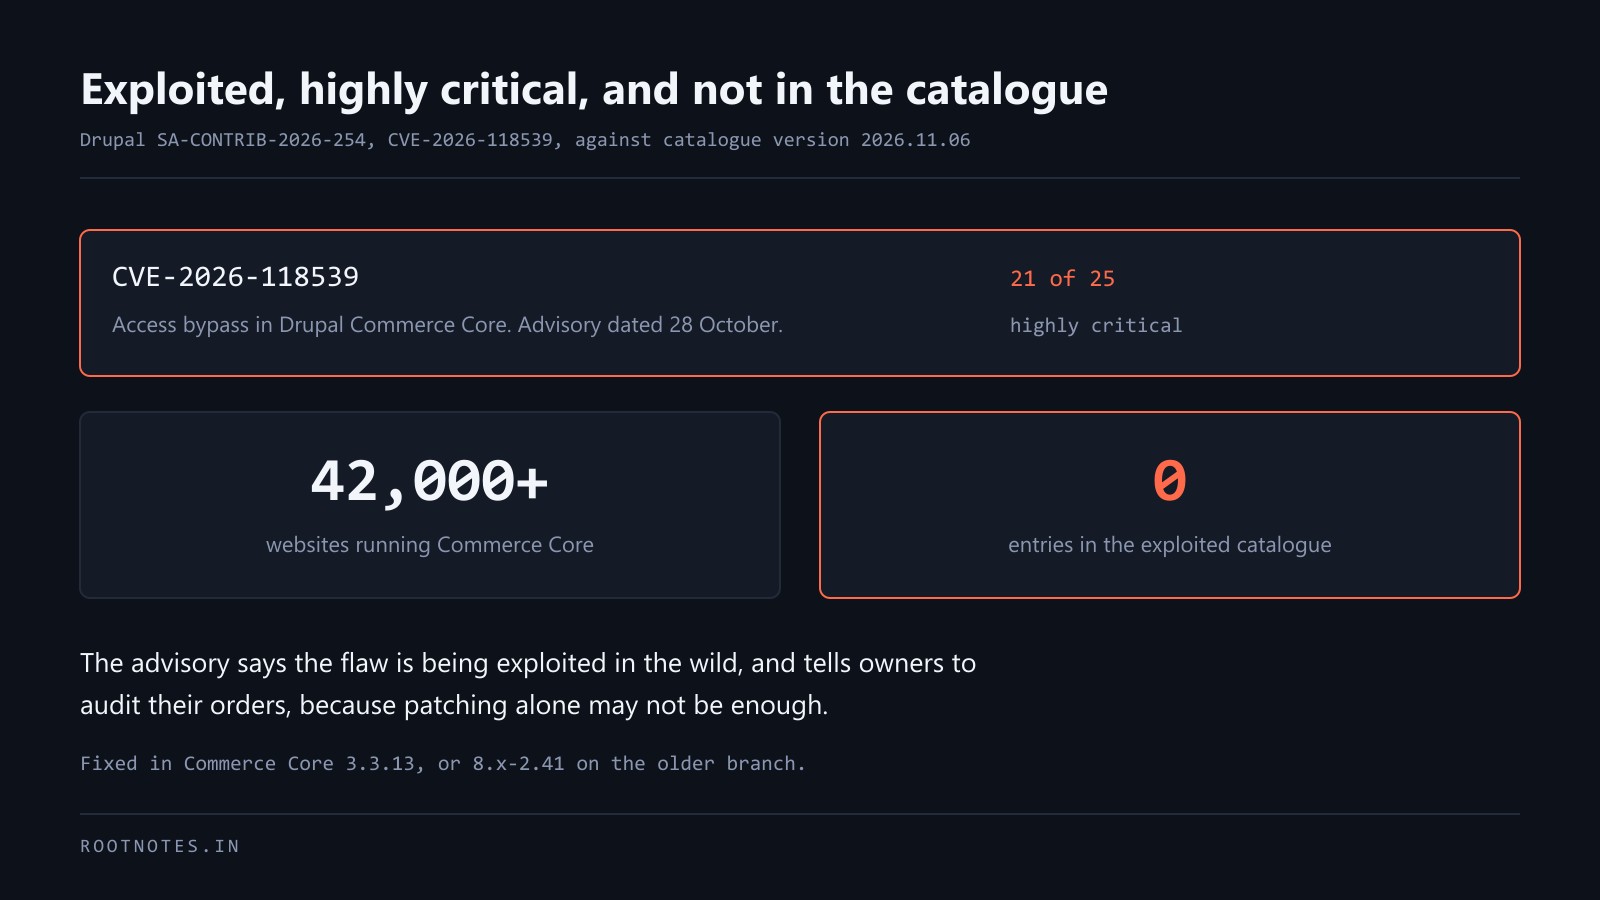
Drupal rates the Commerce Core access bypass highly critical and says it is being exploited in the wild. The fix is one upgrade. The part that will get skipped is the instruction to audit your orders afterwards.
1 article — 2026-11-12
NOT IN CISA KEV — CATALOG 2026.11.18
Authoritative record
Root Notes reports on this identifier; it does not maintain it. For the vendor advisory, the affected versions and the scoring, NVD and MITRE hold the primary records.
Not listed in CISA's Known Exploited Vulnerabilities catalog as of catalog 2026.11.18. That is not evidence it is not being exploited — the catalog records what CISA has confirmed, and identifiers have been attacked for days before appearing in it.
Drupal rates the Commerce Core access bypass highly critical and says it is being exploited in the wild. The fix is one upgrade. The part that will get skipped is the instruction to audit your orders afterwards.