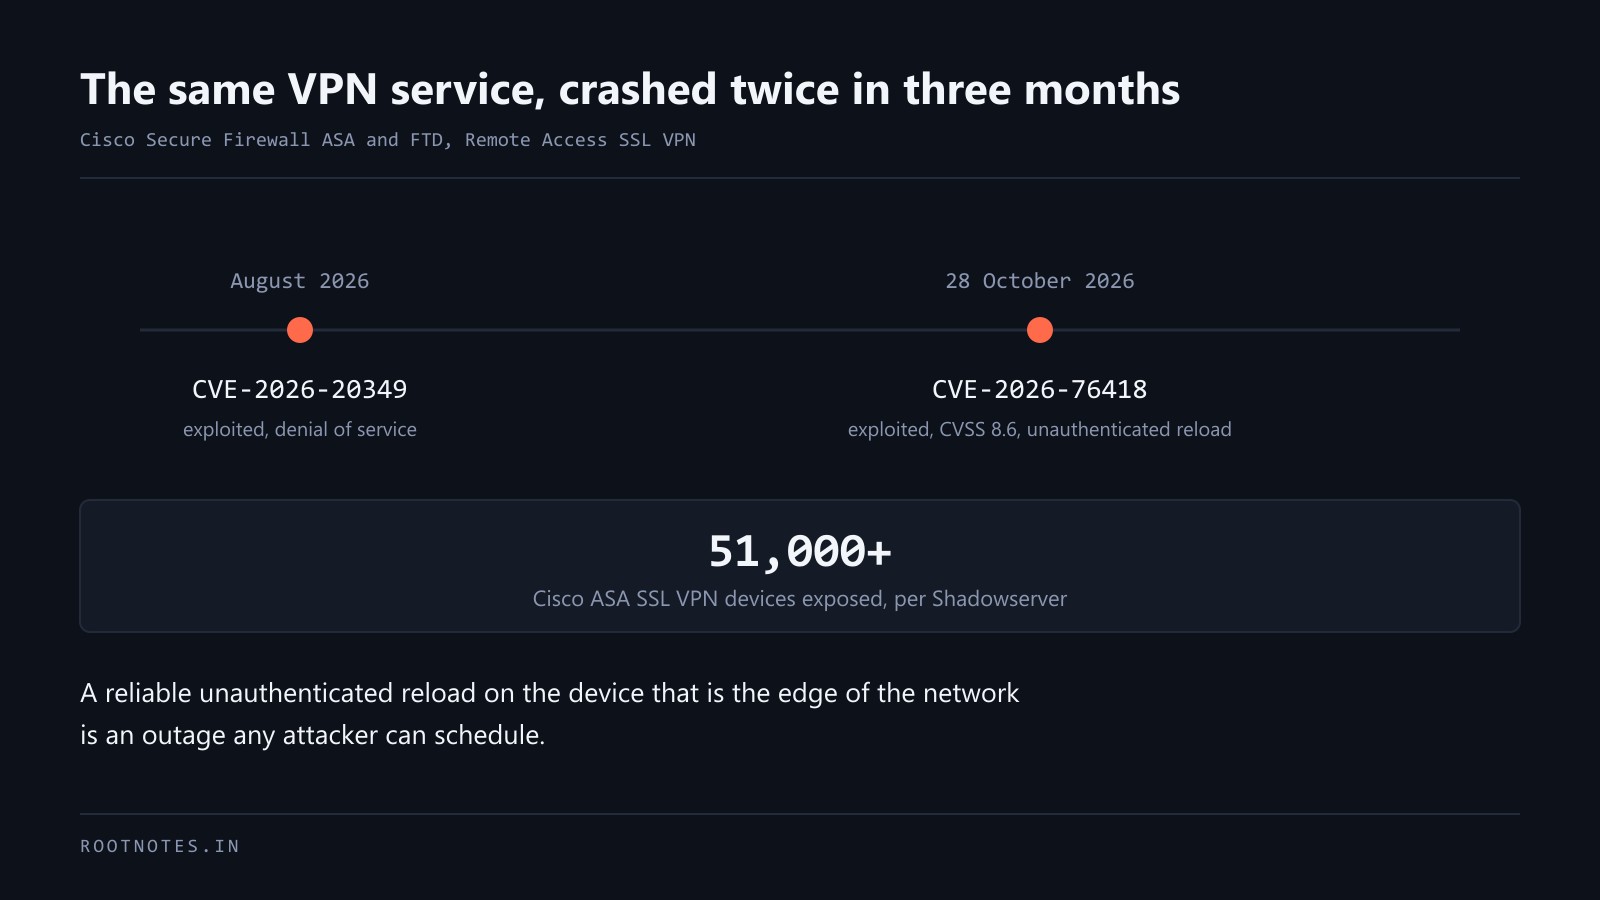
Cisco's VPN service has now been crashed twice in three months
2026-11-12Security
CVE-2026-76418 lets an unauthenticated attacker force an ASA or FTD firewall to reload. In August, a different exploited flaw did the same thing to the same service. Shadowserver counts more than 51,000 of these devices exposed.