The vendor says it has not seen it. The catalogue disagrees.
2026-11-21Security
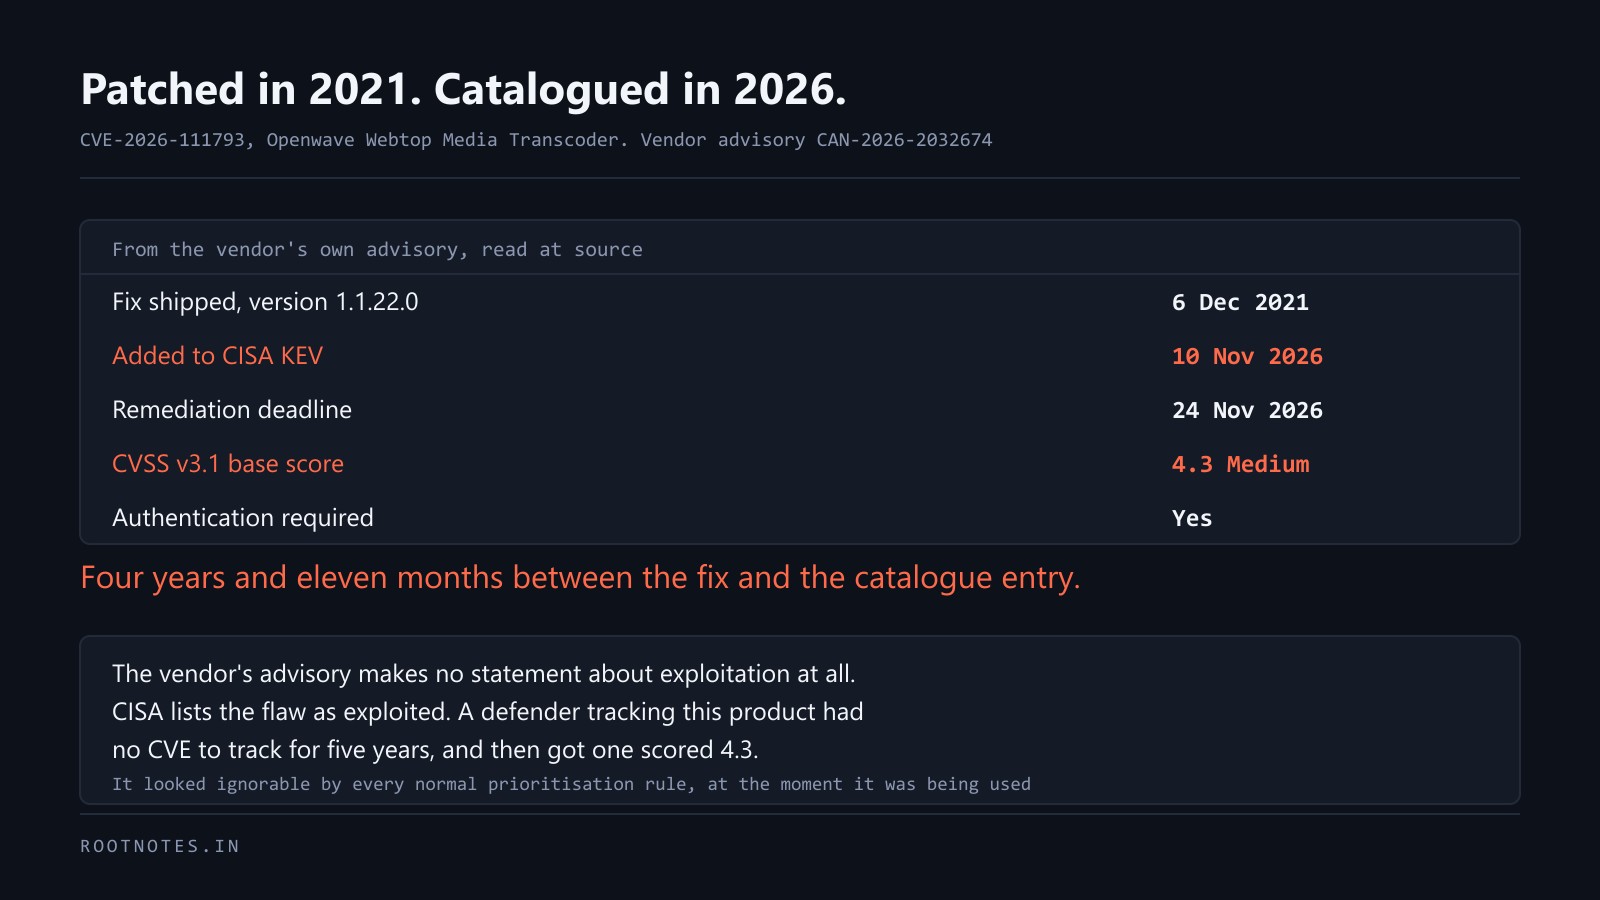
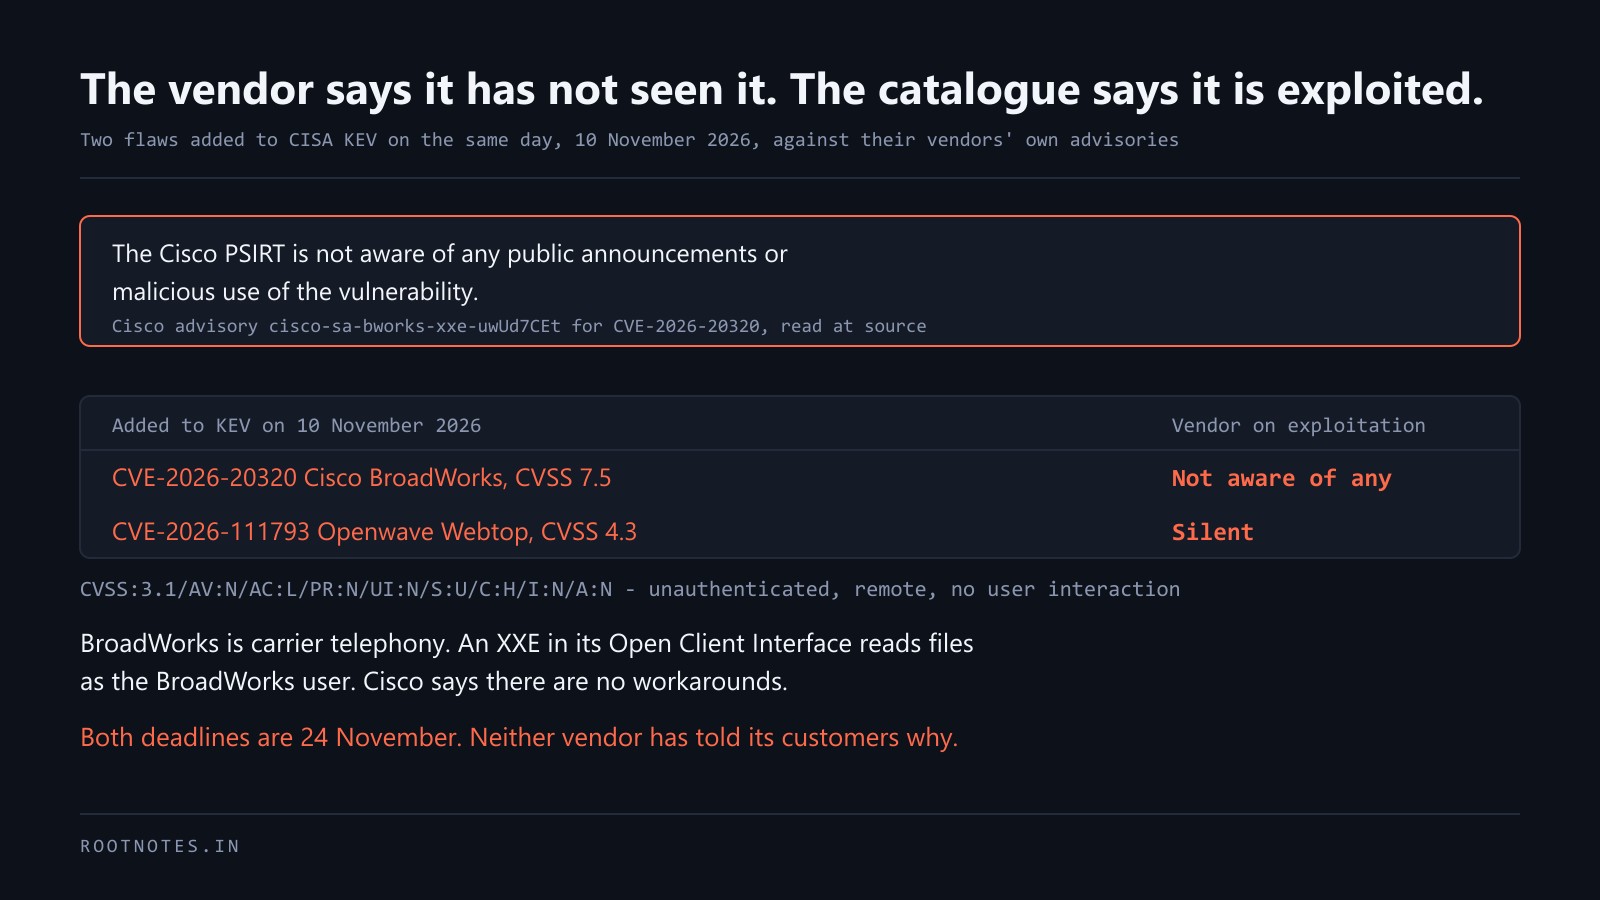
CISA added two flaws to its exploited-vulnerabilities catalogue on 10 November. Cisco's advisory for one of them says its security team is not aware of any malicious use. The other vendor's advisory does not mention exploitation at all.