Skip to content
root notes — archive

ls ./archive --page 7

Archive

page 7 of 17 — 406 articles

The headline price did not move, and the bill fell by a quarter

2026-09-10AI

Claude Fable 5.1 costs exactly what Fable 5 cost per token: 10 dollars in, 50 dollars out. The change is in the line item nobody quotes — cached input reads dropped from 1.00 to 0.25 per million. On agentic workloads, that is most of the input bill.

Nvidia bought the shelf the models sit on

2026-09-10Startups

The 12.93 billion dollar deal for Hugging Face is confirmed in an SEC filing, not a rumour. The company that already sells the hardware models train and run on now owns the place 3 million of them are distributed from — and a hub is not storage, it is the default resolver.

Every Duo hinge is fitted to one housing, and a spare part cannot carry the fit

2026-09-10Gadgets

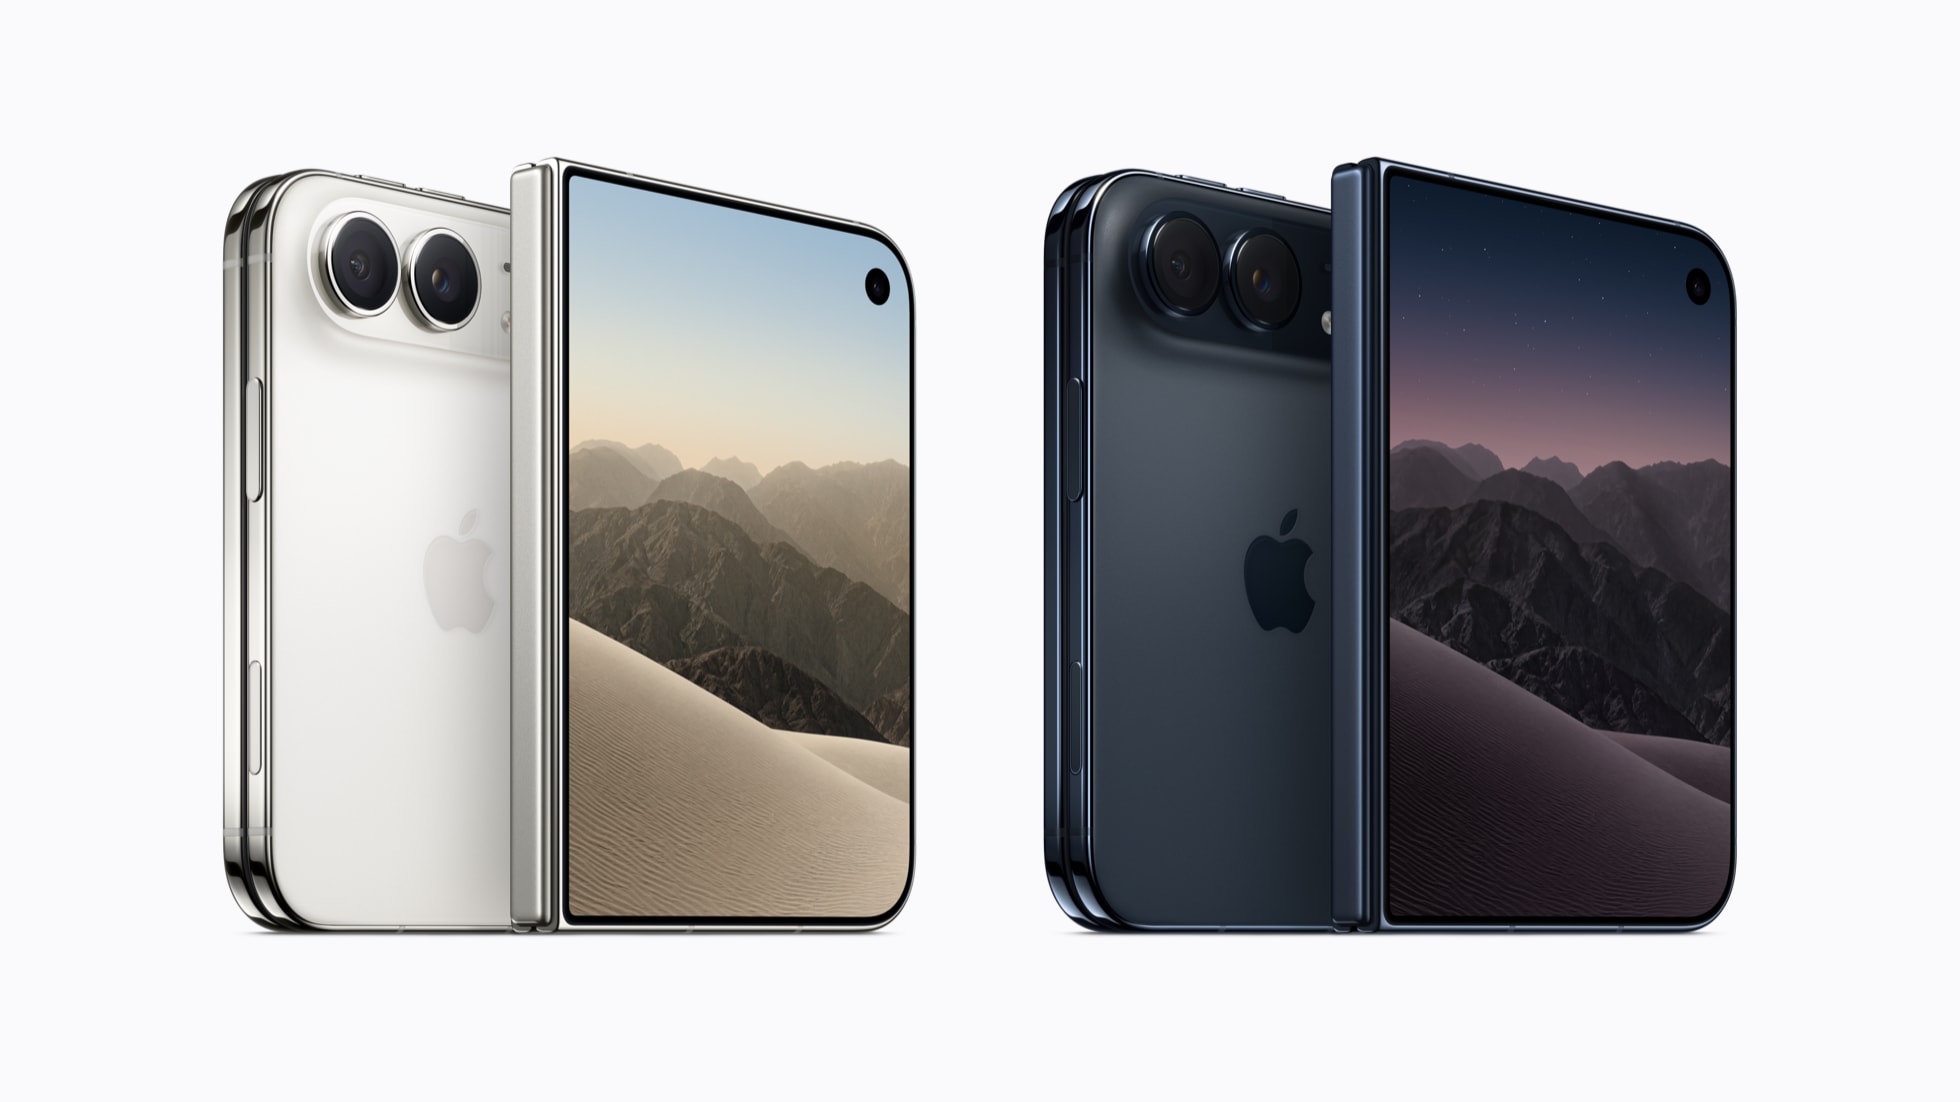
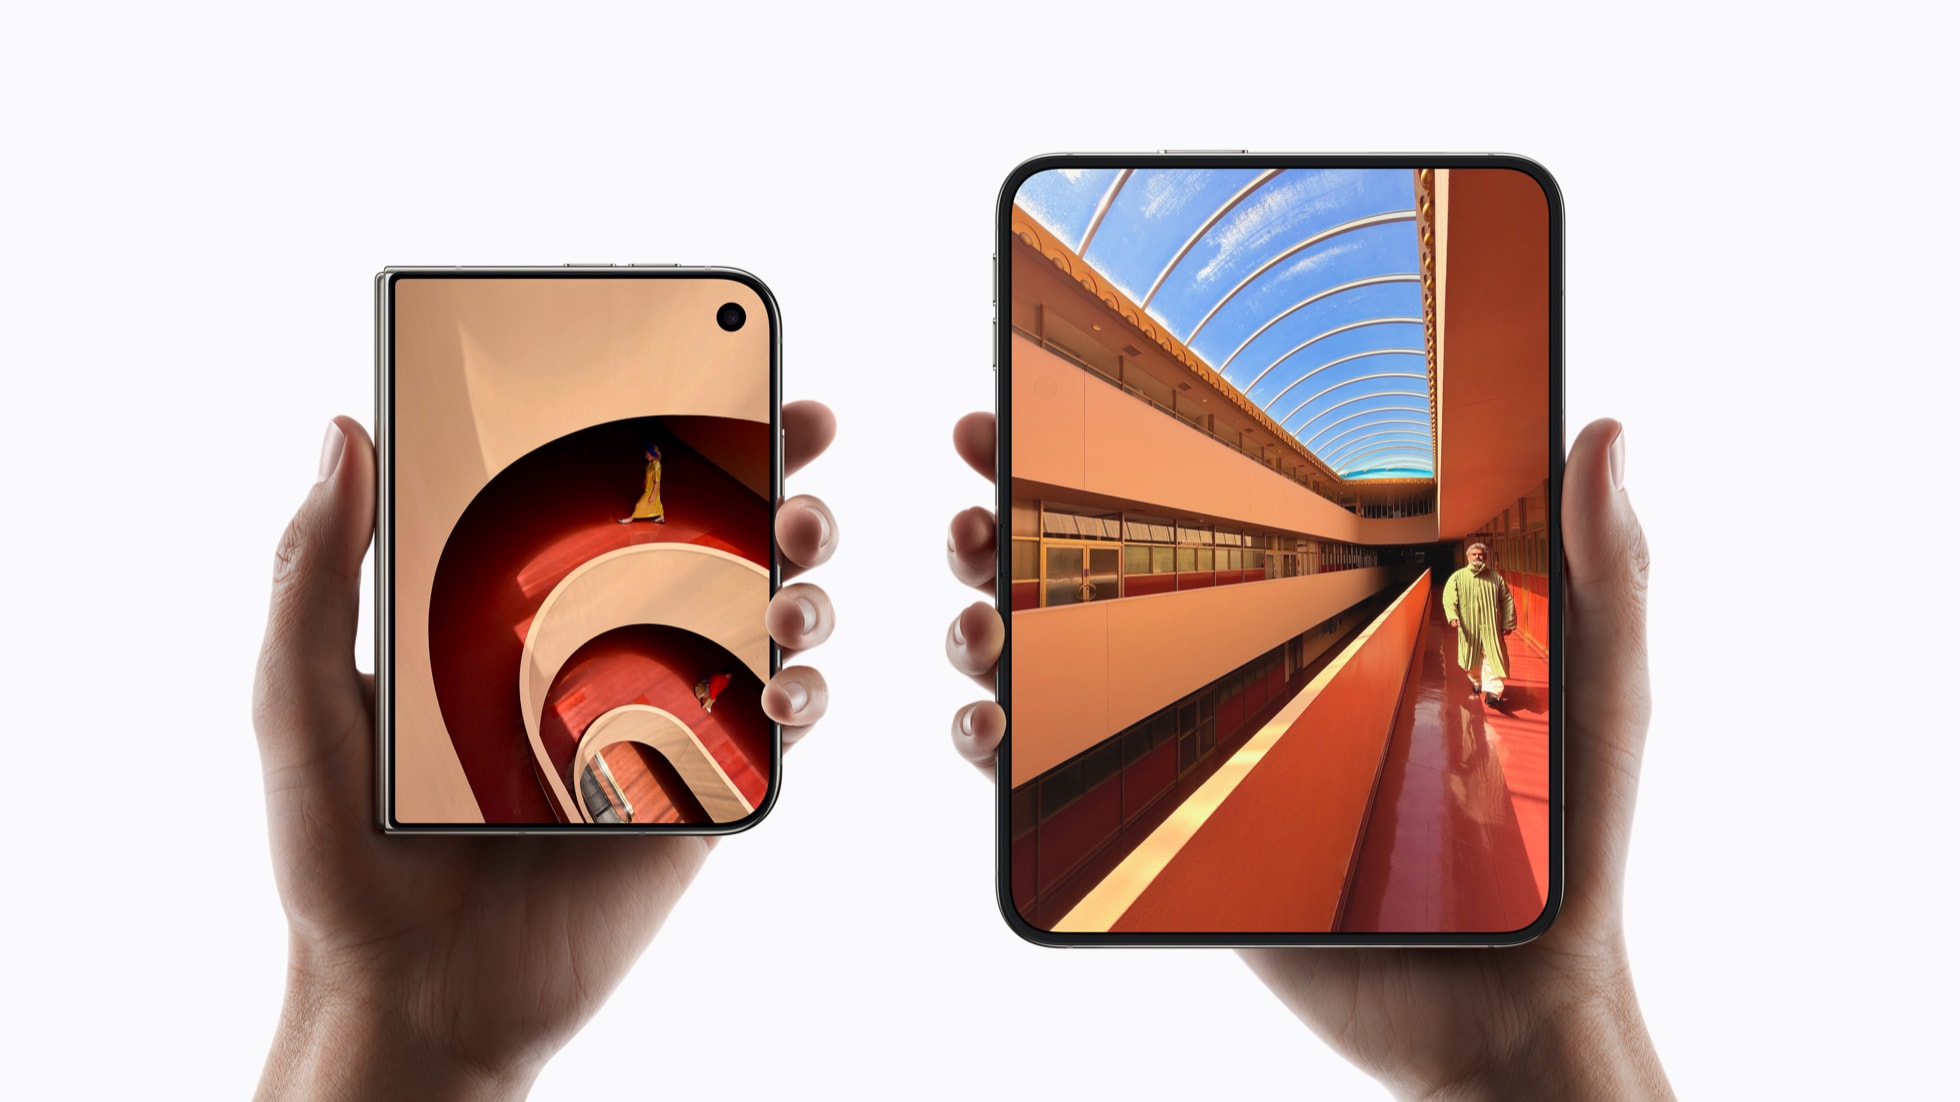
Apple's hardware chief described a hinge assembled per unit: AI matches each hinge to its best-fit housing, a laser scans that individual body, and photopolymer is printed onto it to cancel that body's measured waviness. EU law puts hinge assemblies on the seven-year spare parts list anyway. Both things are true, and they do not fit together.

A terabyte left over four days, and nothing in the chain was a vulnerability

2026-09-10Security

McKesson's 8-K describes roughly one terabyte exfiltrated between 21 and 25 August 2026, detected on the last day. The chain was vishing to Okta SSO to Salesforce and Snowflake — no CVE, no exploit, no patch. And the claimed 284 million records are database rows, by the attackers' own account.

The SAP flaw runs before authentication, so Segregation of Duties does not apply

2026-09-09Security

CVE-2026-44756 is a CVSS 10.0 memory corruption bug in the SAP kernel's Extended Passport handling, reachable with a single malformed header. Onapsis puts the consequence plainly: SAP authorizations and Segregation of Duties will not help, because the vulnerable code runs before any authentication step.

974 flaws, and the two that matter are both privilege escalation

2026-09-09Security

Microsoft patched 974 vulnerabilities in September, a 70% jump over the previous record, with 723 of them in Windows and more than 110 rated critical. Two are being exploited. Both are CVSS 7.8 local privilege escalation, which means the attacker is already on the machine — and that is the whole triage.

The attribution came from commit emails across 84 GitHub accounts

2026-09-09Security

The DFIR Report traced a decade-old Bing poisoning operation — fake activation portals, tech support scams, a custom bot and a Monero miner — to two named companies in Rajasthan, using email addresses left in GitHub commit history. That is a far stronger evidentiary chain than most attribution, and it is worth saying so.

The anonymous client passes the ownership check by being nobody

2026-09-09Security

Two flaws in FreeIPA and 389 Directory Server are unremarkable on their own. Together they let an unauthenticated client write a token entry with blank ownership, satisfy the check for whether it owns that entry, and attach a Kerberos identity with administrative group membership. Nobody has published how to tell whether it already happened to you.

440,000 blocked attempts is a WAF metric, not a compromise count

2026-09-08Security

Wordfence blocked more than 250,000 attempts against Super Forms and more than 190,000 against Elementor Pro. Both flaws are unauthenticated file upload, both are patched, and the Super Forms campaign has been running since 14 July. What nobody has published is how many sites actually fell.

One researcher dropped three exploits. Only Gen Digital has shipped a fix

2026-09-08Security

PrettyPrague, FalconFlank and GreenSection target Avast's sandbox, CrowdStrike Falcon's macro remediation and NVIDIA's display driver. Gen Digital has patched. CrowdStrike's advice is to turn the affected protection off. NVIDIA is still investigating. And the FalconFlank claim this site called single-source last week now has independent confirmation.

Adobe has patched StyleSmuggler. The first confirmed victim was fully patched too

2026-09-08Security

CVE-2026-75650 is rated CVSS 10.0 and Adobe shipped the fix on 8 September, four days into active exploitation. Applying it is only half the remediation — the encryption keys have to be rotated as well. And the first confirmed victim was already running the August patches, which is why patching is not the same as being clear.

Search all 406 articles →