Skip to content
tag — vulnerability-management

grep -rl "vulnerability-management" ./articles

#vulnerability-management

11 articles

The counting spread tripled in a month

2026-11-13Security

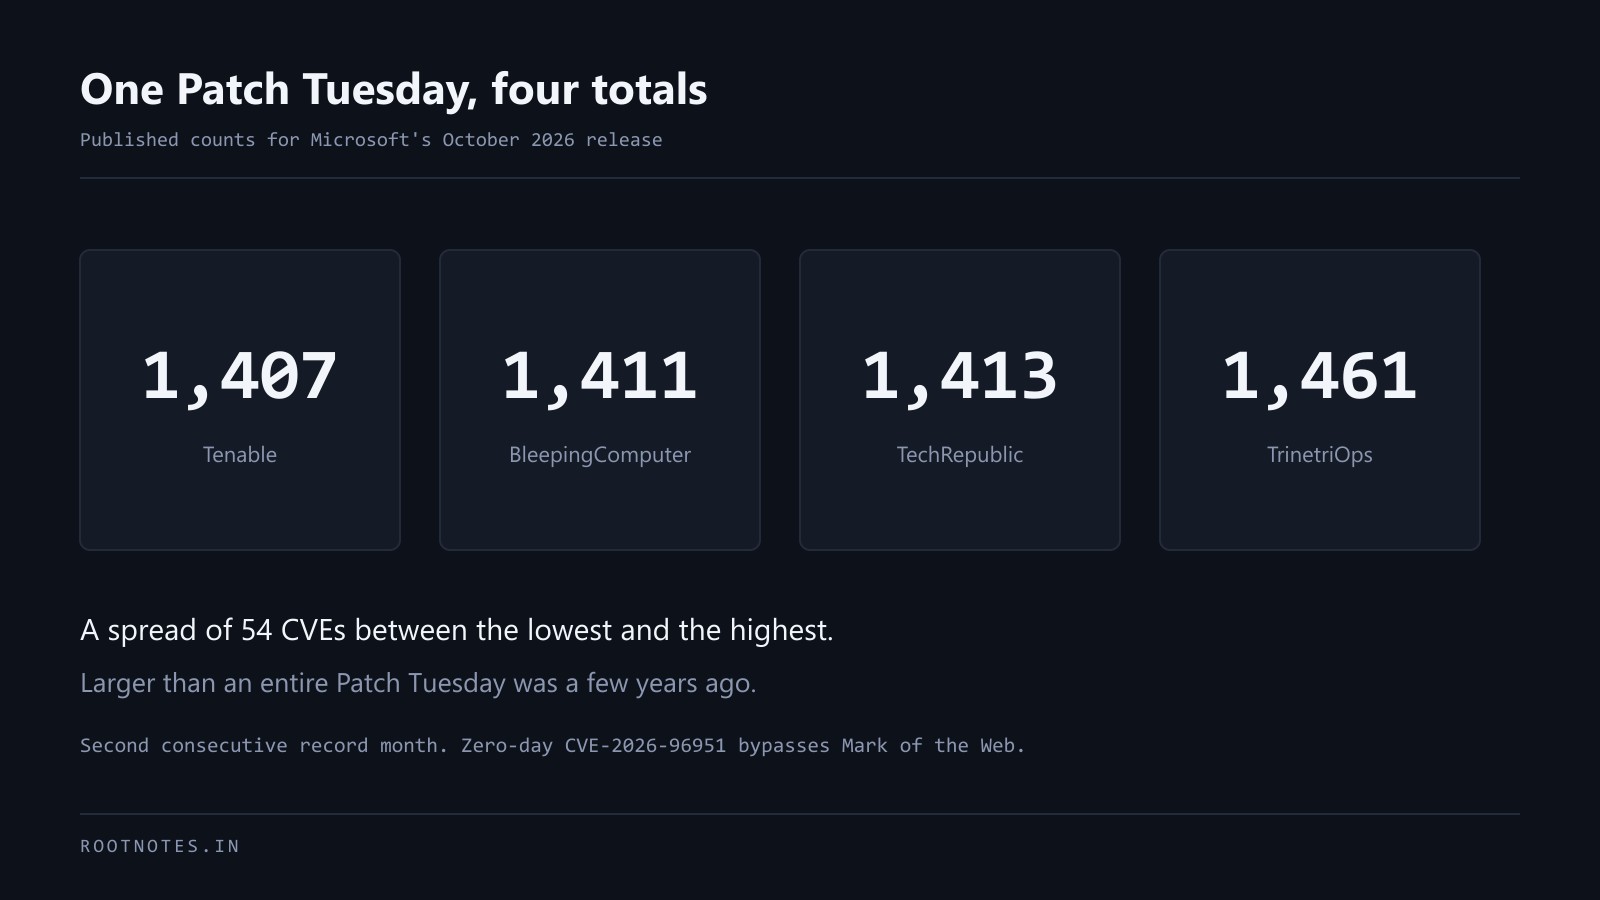
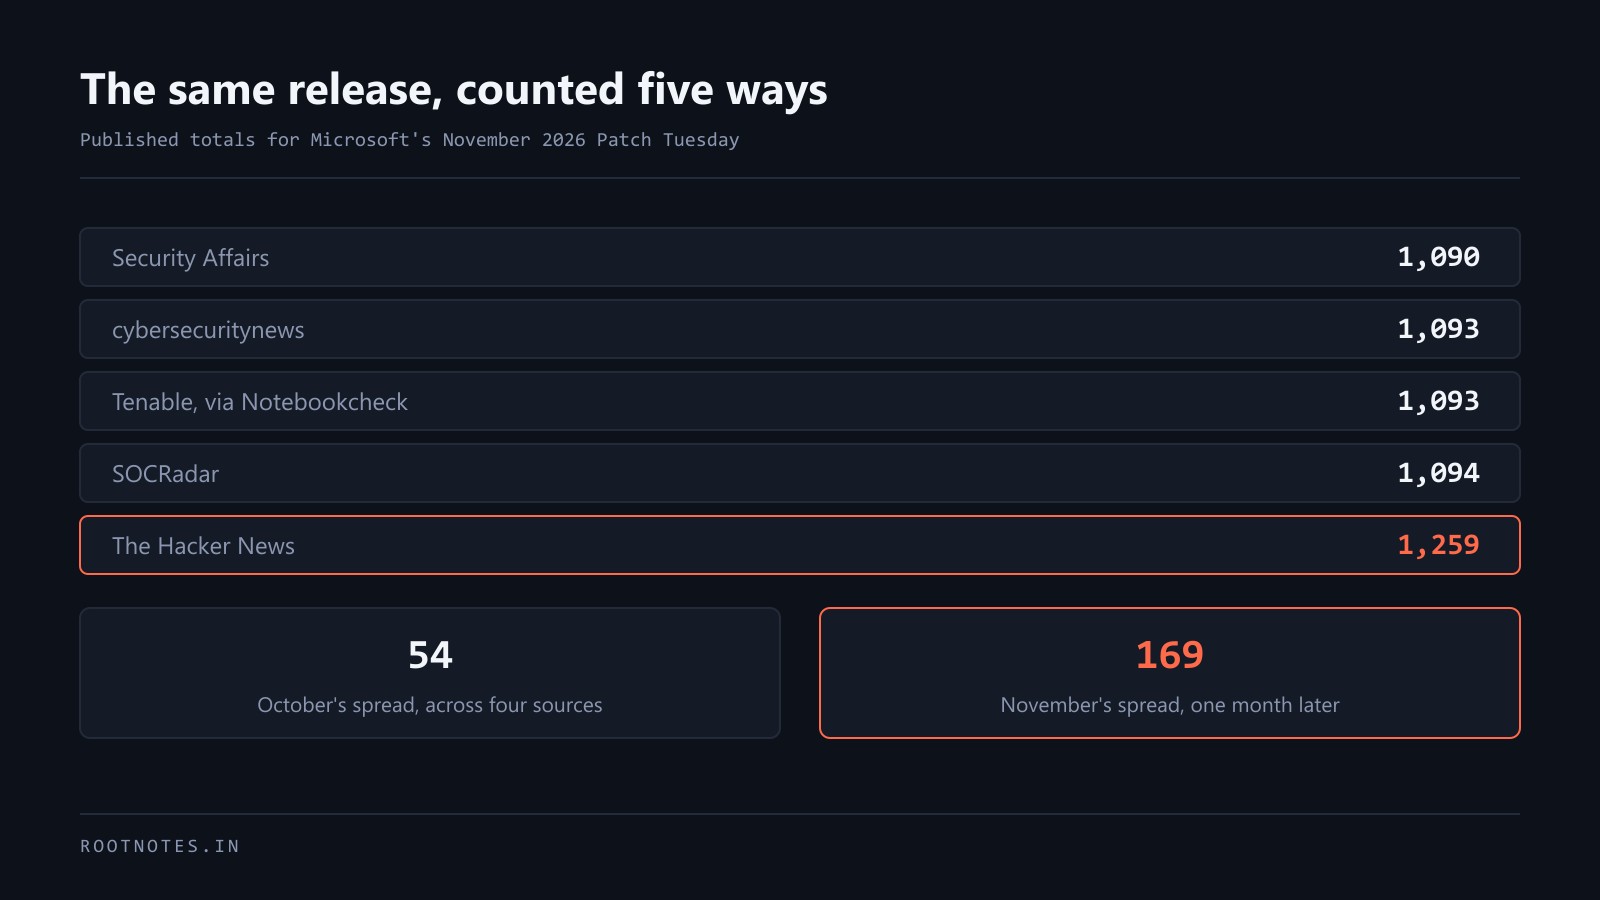
In October four organisations counted the same Patch Tuesday and landed 54 CVEs apart. In November five counted it and landed 169 apart, with four of them clustered and one sitting 165 above the rest.
CISA's three-day patch deadline did not exist before this year

2026-11-09Security

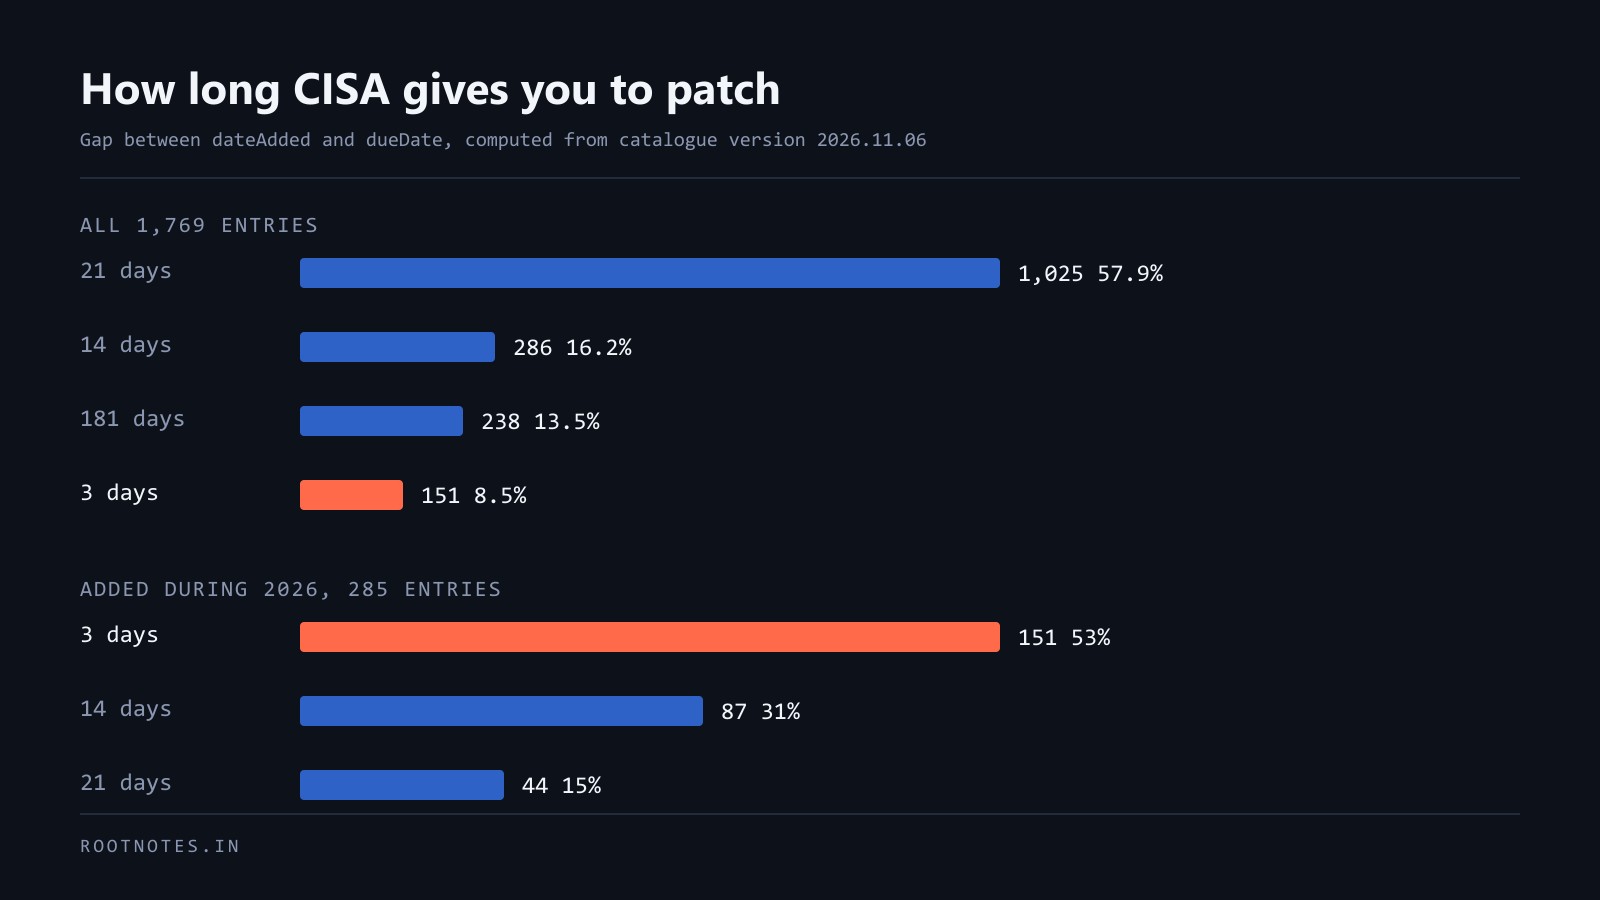
We counted the gap between the date added and the deadline for all 1,769 entries in the exploited vulnerabilities catalogue. Twenty-one days is the historic norm. Every three-day deadline ever issued was issued in 2026, and they are now the majority.

Exploited since January, added to CISA's list in August, due in three days

2026-08-25Security

CVE-2026-21962 is a CVSS 10.0 flaw in Oracle's HTTP Server and WebLogic proxy plug-in. Oracle patched it on 20 January. Exploit code appeared on 22 January and a honeypot logged attacks the same day. CISA added it to the Known Exploited Vulnerabilities catalog on 24 August with a due date of 27 August — and under a directive nobody noticed replacing the old one, agencies now have to check whether they were already breached.